On October 28th I discovered a non-password protected database that contained millions of log files. Upon further research, the records all contained information that identified PrankDial.com as the owner of the data. I immediately sent a responsible disclosure notice and the database was closed for public access shortly after.
According to their website PrankDial is the world’s #1 prank calling service and has sent over 300M calls. Founded in 2006 PrankDial is one of the most well known joke sites sites on the internet. The parent company KickBack Apps (formerly known as TapFury) makes a range of different apps including: PrankPad, Textr, PhoneLine, and PrankDial. I did not see any other references in the records that would indicate that data from the other apps were exposed.
PrankDial lets you:
- Choose from hundreds of prank call scenarios
- Send 3 prank calls for free
- Listen to their reactions afterwards (they are recorded)
- Users get a call history of all their reactions
- Users can submit their reactions so other people can rate/comment on them.
- Users get three free calls a day, if you want to send more calls, you can earn or buy tokens.
What the database contained:
- 138 Million log records in total.
- User emails, credentials and password reset tokens, user IP addresses exposed in the logs.
- Device, operating system and version info.
- Internal IP addresses, Ports, Pathways, and storage info that cyber criminals could exploit to access deeper in to the network.
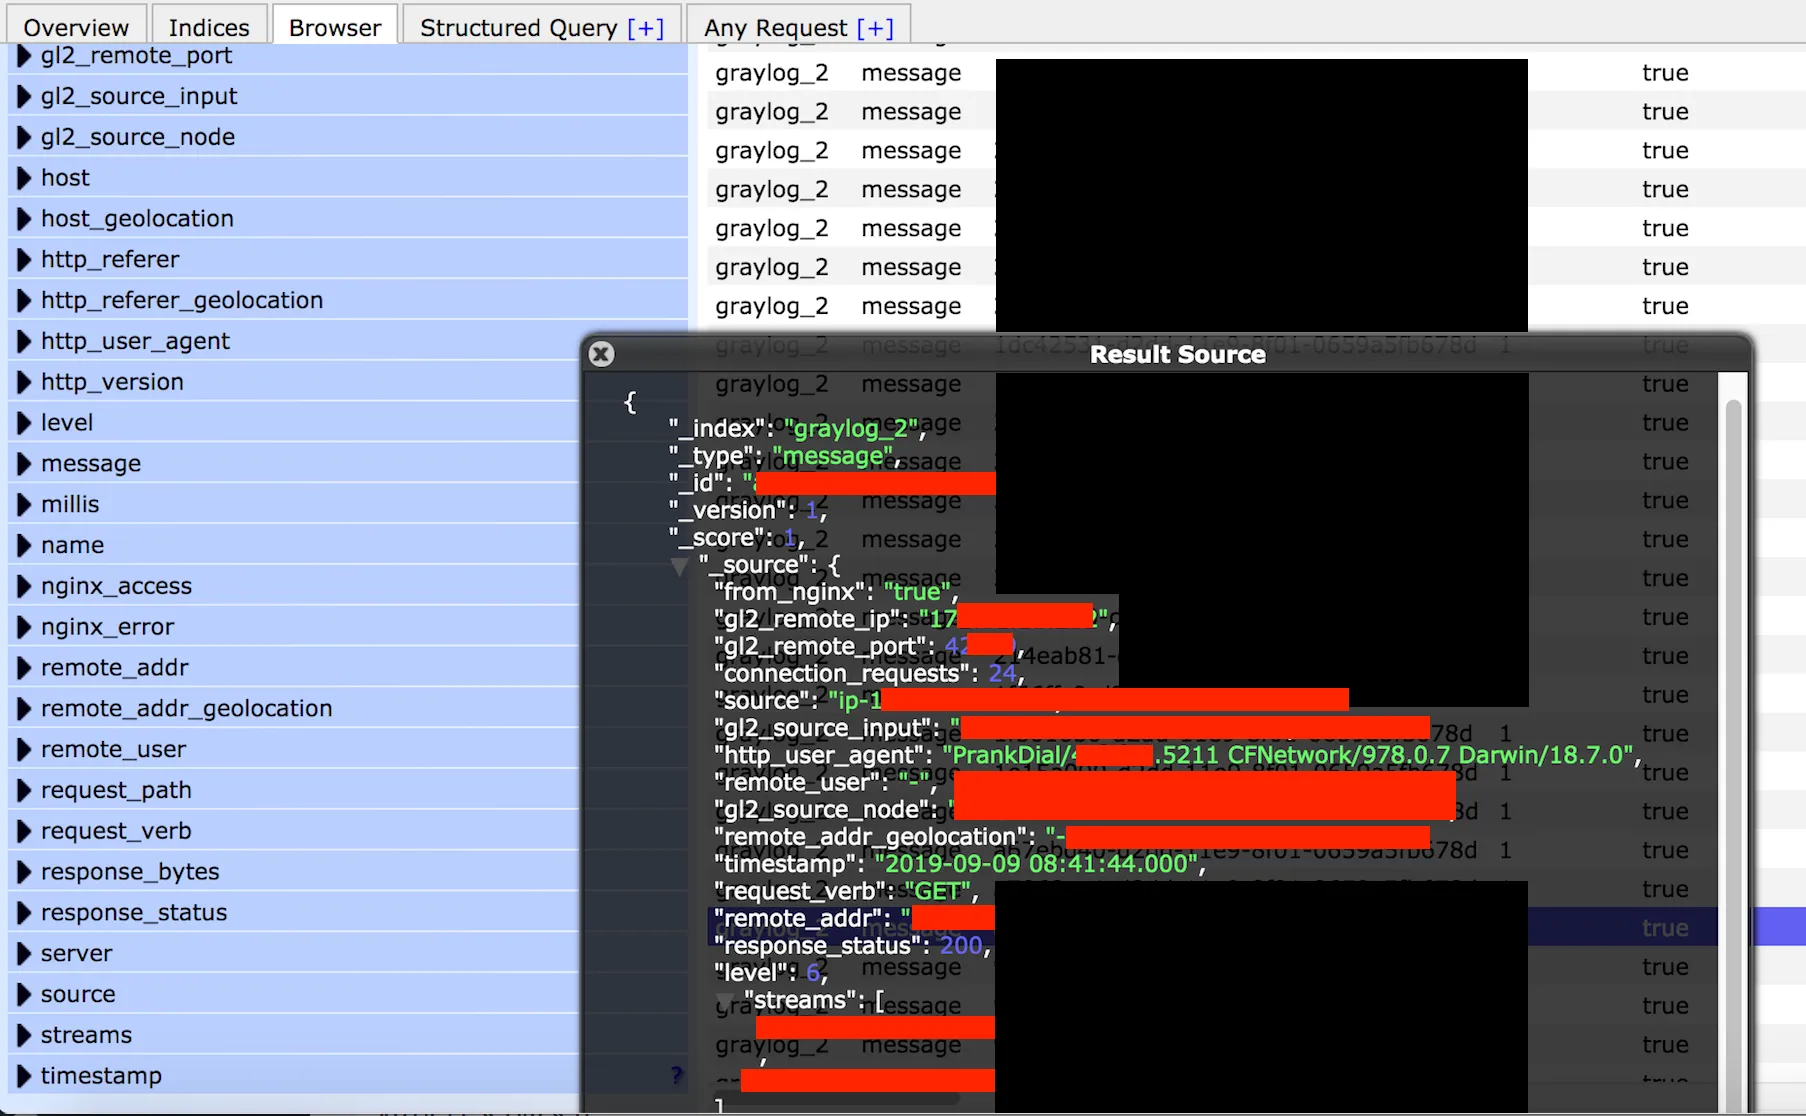
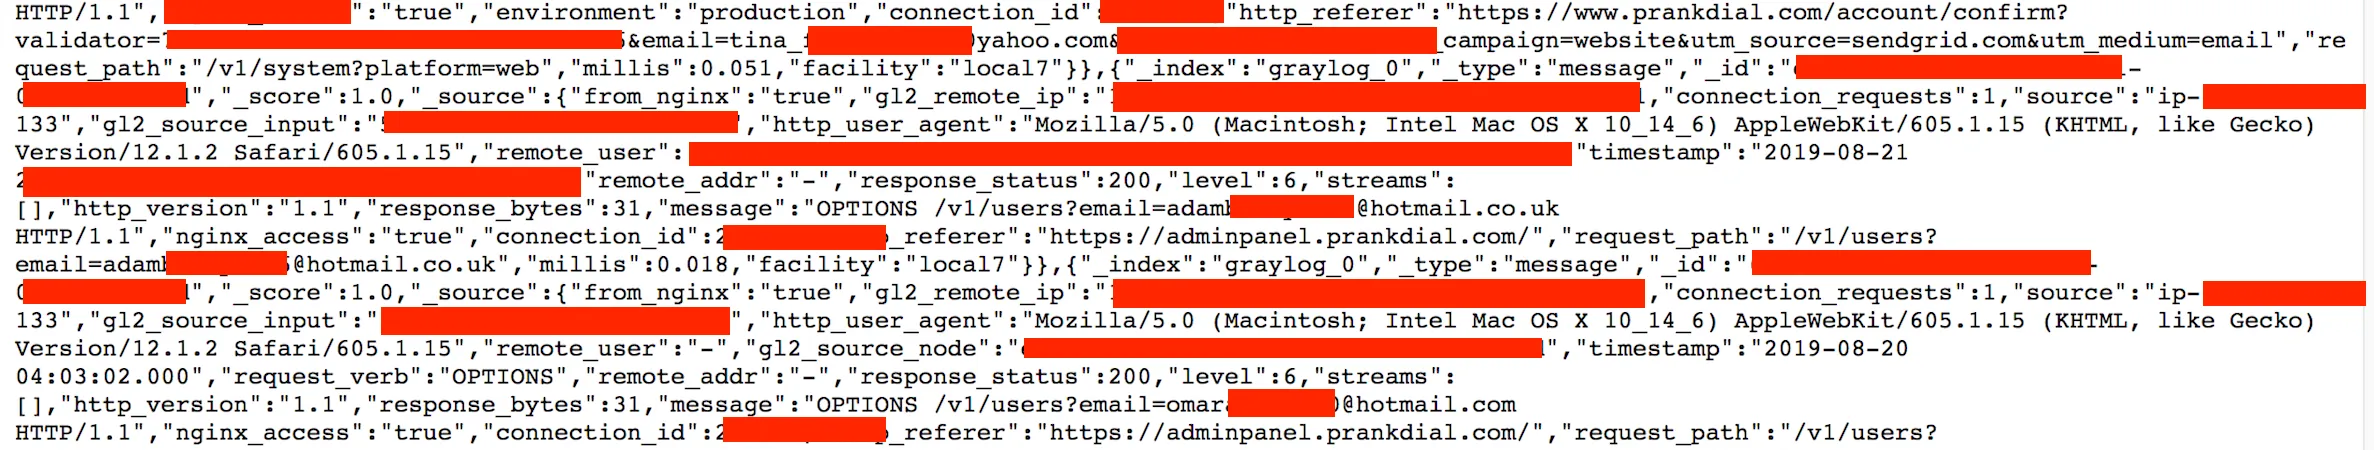
I sent multiple requests to KickBack Apps and PrankDial but no one every replied or acknowledged my discovery, instead they simply closed public access to the logs. It should be noted that I did not see phone numbers. I can only assume that the numbers are routed through a VOIP server and did not appear to be part of this dataset. At the time of publication no statement has been given by KickBack Apps / PrankDial and I will update the article in the event we are provided any statement or more details.
